
"A webhook with no signature check is a public API with extra steps."
n8n makes it easy to wire a webhook to a workflow in minutes. It does not make security the default — that's on the person building it. This checklist covers the ingress boundary most workflows get wrong, and the credential-handling mistakes that follow.
1. Ingress Validation
Every inbound webhook should be authenticated before the workflow body executes — not after. Signature verification (HMAC) plus timestamp/nonce checking closes both spoofed-caller and replay-attack paths in one gate.
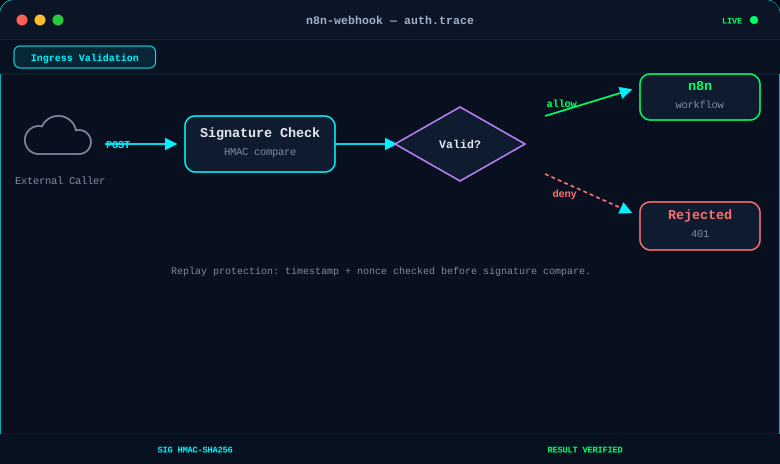
Security Principle
Validate before you trigger — not inside the first node of the workflow.
2. Credential Handling
- Never inline secrets in a workflow's JSON — use n8n's credential store, not hardcoded values in a node.
- Scope credentials narrowly: a workflow that only needs read access shouldn't hold a write-capable API key.
- Rotate on personnel change: a shared workflow credential outlives the person who set it up unless rotation is a process, not an afterthought.
3. Practitioner Checklist
| Check | Why it matters |
|---|---|
| Webhook signature verified before workflow logic runs | Blocks spoofed and forged trigger events |
| Timestamp + nonce checked (replay protection) | Stops a captured legitimate request being resent |
| Credentials in n8n's store, not inline | Prevents secret leakage via exported/shared workflow JSON |
| Workflow permissions scoped to minimum need | Limits blast radius if a single workflow is compromised |
| Error/dead-letter path doesn't leak secrets in logs | Debug logs are a common accidental leak surface |
4. What This Is Not
This is not a case against automation platforms — n8n is capable, production-grade tooling. The gap is that convenience defaults are not security defaults, and the team building the workflow is responsible for the difference.
Skills Demonstrated: Workflow Security · API Authentication · n8n Architecture Review
Related service: Secure Automation & AI Workflow Review · Companion engineering: Harrison Ndeke's n8n services