Home > Proof

Verified Technical Proof & Case Studies

// Proof Before Promotion 路 Machine Learning NIDS 路 Live Client Engagements 路 Zero-Trust Systems

82,332
Evaluated UNSW-NB15 Benchmark Flows
100%
Human-Verified Vulnerability Findings
Zero
Unsolicited Scanning or Client Data Retained
Production
Verified Client Deployments on Vercel & Cloud
Flagship ML Research & Implementation Final Year Cybersecurity Project

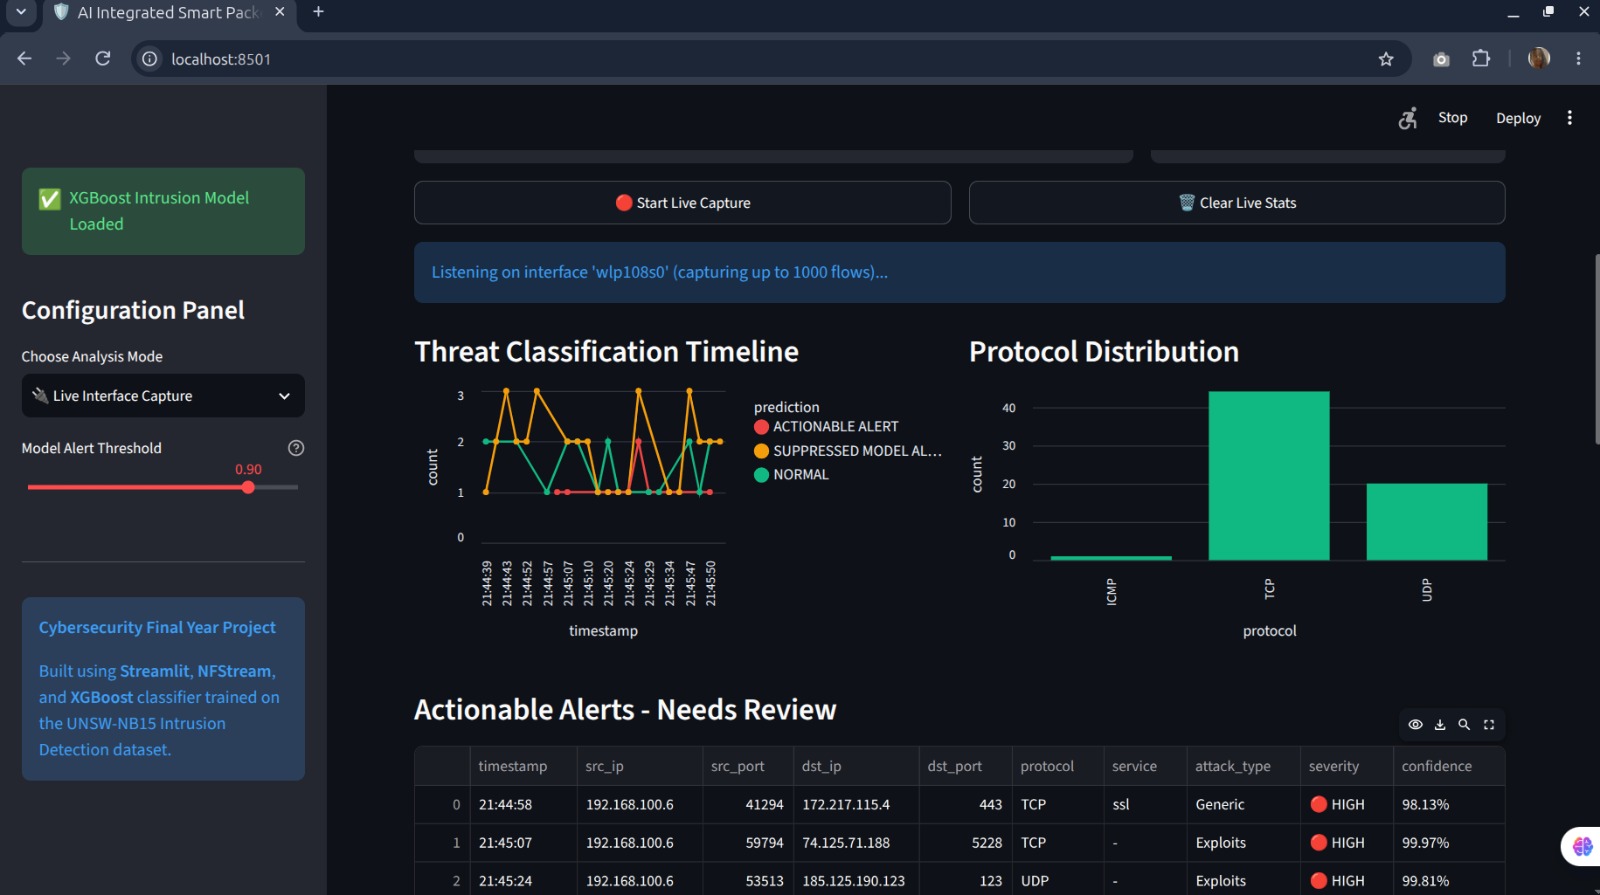
AI Integrated Smart Packet Analyzer

A high-performance Machine Learning Network Intrusion Detection System (NIDS) designed to analyze network flows in real time, distinguish malicious traffic from normal operations, categorize threats, and provide explainable attribution behind every prediction.

  • Evaluated on 82,332 held-out UNSW-NB15 benchmark network flows with high precision.
  • Binary attack detection and multi-class threat classification powered by XGBoost.
  • Real-time packet inspection via NFStream and Scapy with explainable prediction scoring.
  • SOC-style triage dashboard with exportable incident logs and PDF/CSV compliance reports.
PythonXGBoostStreamlitNFStreamScapyThreat Intelligence
Read the Full Case Study → View Code on GitHub
Active Client Delivery Commercial Delivery Record

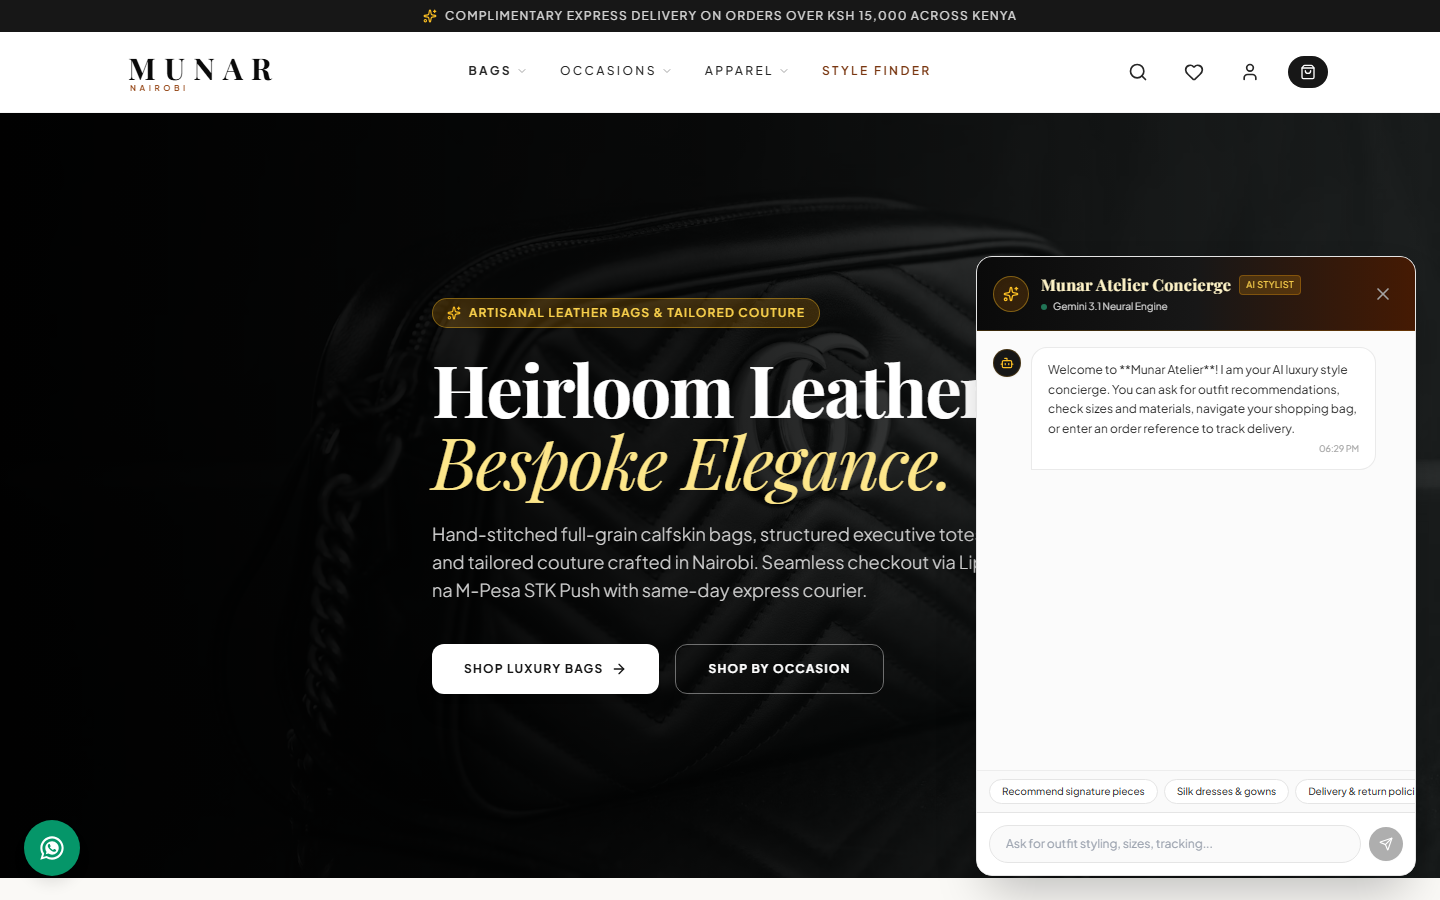
Munar: Website Audit, Optimization & Deployment Handover

Collaborative delivery project with Harry Ndeke for Munar (munar-ke.vercel.app). Managed the security baseline, content structure, UX clarity, accessibility, technical SEO foundations, and production deployment on Vercel.

  • Established baseline audit across performance, mobile responsiveness, and security headers.
  • Enforced strict security boundary: scoped reviews without intrusive unauthorized scanning.
  • Implemented structured data, canonical URLs, and clean analytics without tracking leaks.
  • Delivered complete client access, documentation, and maintainable handover record.
Client DiscoverySecurity BaselineTechnical SEOUX / Mobile AuditingVercel
Read the Full Case Study → View Munar Deployment
HarLyn Internal Product · Built & Tested Zero-Trust Data Protection Engine

TrustCapsule: Zero-Trust Data Protection & Compliance Engine

Data escrow and regulatory compliance engine built with Harry Ndeke under HarLyn Digital Partners. Wraps outbound sensitive files into self-destructing, watermarked, tamper-proof capsules with automated Kenya ODPC, GDPR, and HIPAA compliance certificates.

  • AES-256-GCM encryption at rest, forced row-level security (RLS), zero permissive policies.
  • Append-only HMAC-SHA256 audit chain — even the database service role cannot rewrite history.
  • 256-bit recipient access tokens, never logged, only stored as a cryptographic hash.
  • Compliance certificates generated from real audit-chain data, not asserted claims.
Next.js 15Supabase / Postgres RLSAES-256-GCMChrome ExtensionWordPress Integration
Read the Full Case Study →
In Active Development AI-Assisted Security Monitoring Platform

HarLyn Sentinel: AI-Assisted Security Monitoring Platform

Managed threat-detection and SOC platform in active development with Harry Ndeke, combining Wazuh telemetry with AI-enriched alerting and automated n8n response workflows — designed for businesses without an in-house SOC.

  • Wazuh-powered log analysis, file integrity monitoring (FIM), and vulnerability scanning.
  • AI Security Analyst converts raw alerts into plain-English risk context and attack-chain mapping.
  • Red-team / blue-team simulation lab for validating detection rules before customer rollout.
  • Separate SOC console and client executive dashboard with monthly compliance reporting.
WazuhNext.js 15n8nMulti-Tenant Architecture
Read the Architecture Record →
Defensive Operations & IR SOC Analyst Investigation Records

Incident Response Walkthroughs & Technical Reports

Practical investigations and defense methodologies analyzing real-world attack vectors, log forensics, and network security boundary enforcement.

  • Portal Drop Web Shell Incident: Correlating Apache access logs with EDR telemetry to triage brute-force ingress, Base64 RCE web shells, and reverse-shell containment.
  • Extending Your Network Security Boundary: Port forwarding, stateful vs stateless firewalls, VPN tunnels, and L2/L3 topology unified into defensive architecture.
Apache Log TriageMITRE ATT&CKEDR TelemetryVPN ArchitecturesFirewalls
View Portal Drop Walkthrough → View Network Boundary Notes → 馃搫 Download Network PDF (1.8 MB)
See what else is currently in development in our labs →
NEED VERIFIABLE SECURITY ASSURANCE?

Let's Review Your Architecture

Book a scoped consultation call with Nazline Mwita to assess your digital workflows, data protection compliance, or web/API security.

Book Consultation → Browse All Services
WhatsApp