Nazline Mwita - Cybersecurity & Assurance Lead
CO-FOUNDER & LEAD

Nazline Mwita — Cybersecurity Assurance Lead & Data Protection Auditor in Kenya

Co-Founder & Cybersecurity Assurance Lead
Co-founding partner alongside Harrison Ndeke · Building secure AI-powered websites, automations & resilient workflows.
Nairobi / Thika, Kenya
Authorized Security Assessments B.S. Computer Science Responsible Disclosure
Assurance Console (Interactive v2.0)

Nazline Mwita: Security Assurance & Advisory Console

Working Positioning: "We help growing organisations build secure AI-powered websites, automations and digital workflows, then document, test and hand them over responsibly."

Type help to explore services, audit methods, and professional background.

client@assurance:~$

PRACTITIONER OVERVIEW Assurance Leadership & Operating Model

Practitioner
Nazline Mwita
Consulting Role
Co-Founder & Cybersecurity Assurance Lead
Assessment Focus
Authorized web and API security assessments
Operating Rule
Clarity before branding · Proof before promotion

Nazline Mwita is a Nairobi-based Cybersecurity Assurance Lead and Co-Founder at HarLyn Digital Partners specializing in data protection site audits, secure API and workflow audits, machine learning network intrusion detection (NIDS), and defensive architecture for African enterprises.

I lead the cybersecurity and technical assurance practice at HarLyn Digital Partners. Working alongside Harrison Ndeke, I ensure that as organisations adopt AI assistants, automated integrations, and modern web architectures, they do so with rigorous security boundaries and zero-trust data protection.

"Many providers build websites, automate workflows, or conduct security reviews in isolation. At HarLyn Digital Partners, we treat security, automation, and maintainability as one continuous system: map → secure → build → test → document → hand over."

Rather than relying on generic scanner output or fear-based sales tactics, my work is grounded in verifiable evidence, authorized scopes, technical data-protection checks, and clear remediation pathways that non-technical decision-makers can trust.

Core Assurance Domains

Authorised Security Audits

Scoped web application, API, and cloud configuration assessments conducted under written rules of engagement.

Automation & Data-Flow Hygiene

Reviewing webhook endpoints, credential storage, and least-privilege tool execution for n8n and autonomous agents.

Evidence-Led Threat Analysis

Human-verified vulnerability triage and realistic severity rankings that separate real exploit paths from vanity alerts.

Governance & Responsible Handover

Clear remediation roadmaps, data protection audit findings with fixes, and comprehensive operational documentation.

View Full Practitioner Profile & Bio →

CONSULTING PRACTICE Services & The Entry Offer

We serve SMEs, startups, and established teams that need to replace manual bottlenecks with reliable digital workflows without exposing customer data, API keys, or operational stability.

RECOMMENDED FIRST ENGAGEMENT

Secure Digital Workflow Assessment

Fixed Scope · 2 to 3 Weeks Delivery

A fixed-scope discovery engagement that maps one critical workflow, public web surface, or internal API; identifies security and operational vulnerabilities; ranks high-ROI automation opportunities; and delivers an actionable 30/60/90-day remediation and implementation roadmap.

Current-State Architecture Map End-to-end trace of your data flows, external integrations, and sensitive data touchpoints.
Authorised Security Observations Human-verified risk findings on configurations, permissions, and exposed surfaces within agreed scope.
Automation & AI Feasibility Matrix Prioritised evaluation of automation opportunities ranked by business value, operational risk, and implementation effort.
Actionable Remediation & Build Roadmap Concrete 30/60/90-day plan with clear stop-points, owner assignments, and safe implementation paths.
Request Scoping Call Zero obligation to proceed with follow-on builds. Clear decisions before code.

The Firm's Four Service Pillars

01

Secure AI-Powered Websites

Modern business and service websites built for speed, conversion, and durability. Includes guided search assistants, lead capture integrations, and technical SEO/AEO foundations.

Led by Harrison · Audited by Nazline
02

AI & Workflow Automation

Robust n8n workflow architecture, multi-step integrations, and RAG knowledge systems that eliminate manual data re-entry while maintaining strict operational audit trails.

Led by Harrison · Audited by Nazline
03

Authorised Security Services

Scoped website, web application, and API assessments with formal rules of engagement. Practical remediation reports that explain risks in plain business language.

Full service details → Led by Nazline
04

Secure Automation Reviews

Data-flow, webhook, and permission reviews for automated systems. Setting tool-execution boundaries, credential hygiene, and human approval checkpoints for AI agents.

Full service details → Led by Nazline

Additional Focus Areas

AI Security Kenya

Product-level AI security: model access control, prompt-injection exposure, data leakage, and vendor API key hygiene.

Full service details → Led by Nazline

RAG Security

Vector database access control, source-freshness and provenance, indirect prompt injection, and RBAC metadata filtering.

Full service details → Led by Nazline

AI Agent Security

Tool-call permission boundaries, human-approval gates, trajectory auditing, and sandboxing for autonomous AI agents.

Full service details → Led by Nazline

Security Audits Kenya

Infrastructure and cloud configuration review, security architecture review, and process/policy audits.

Full service details → Led by Nazline

Data Protection Site Audit

Technical audit of a website's data handling — forms, cookies and consent, encryption, access controls, third-party sharing and breach logs — with findings and a fix list. Technical checks only, not legal advice.

Full service details → Led by Nazline

Cybersecurity Consultant Kenya

Ongoing fractional security advisory — roadmap planning, policy, vendor risk review, and incident-readiness.

Full service details → Led by Nazline
Browse Full Services & Methodology Catalog →

ETHICAL STANDARDS Responsible Security Boundary & Charter

Cybersecurity capability is valuable only when governed by discipline and ethics. We hold ourselves to clear, published boundaries:

STANDARD PROTOCOL

Permission Before Testing

Active security testing is conducted strictly under written client authorization that defines exact targets, methodology, testing windows, and emergency stop conditions.

STRICTLY PROHIBITED

No Unsolicited Scans

We do not perform unsolicited active scanning against arbitrary websites, nor do we use automated scanner dumps to manufacture panic or pressure prospective clients.

STANDARD PROTOCOL

Human Evidence Verification

Every finding reported to a client is manually reproduced and evaluated for actual business impact. We measure trust and clarity rather than inflated vanity metrics.

STANDARD PROTOCOL

Data Minimization & Privacy

We never extract, download, or retain client data to "prove" impact. All assessment evidence is handled with least privilege and securely deleted per our retention policy.

VERIFIED PROOF Technical Proof & Active Deliveries

Research & Implementation Final Year Cybersecurity Project

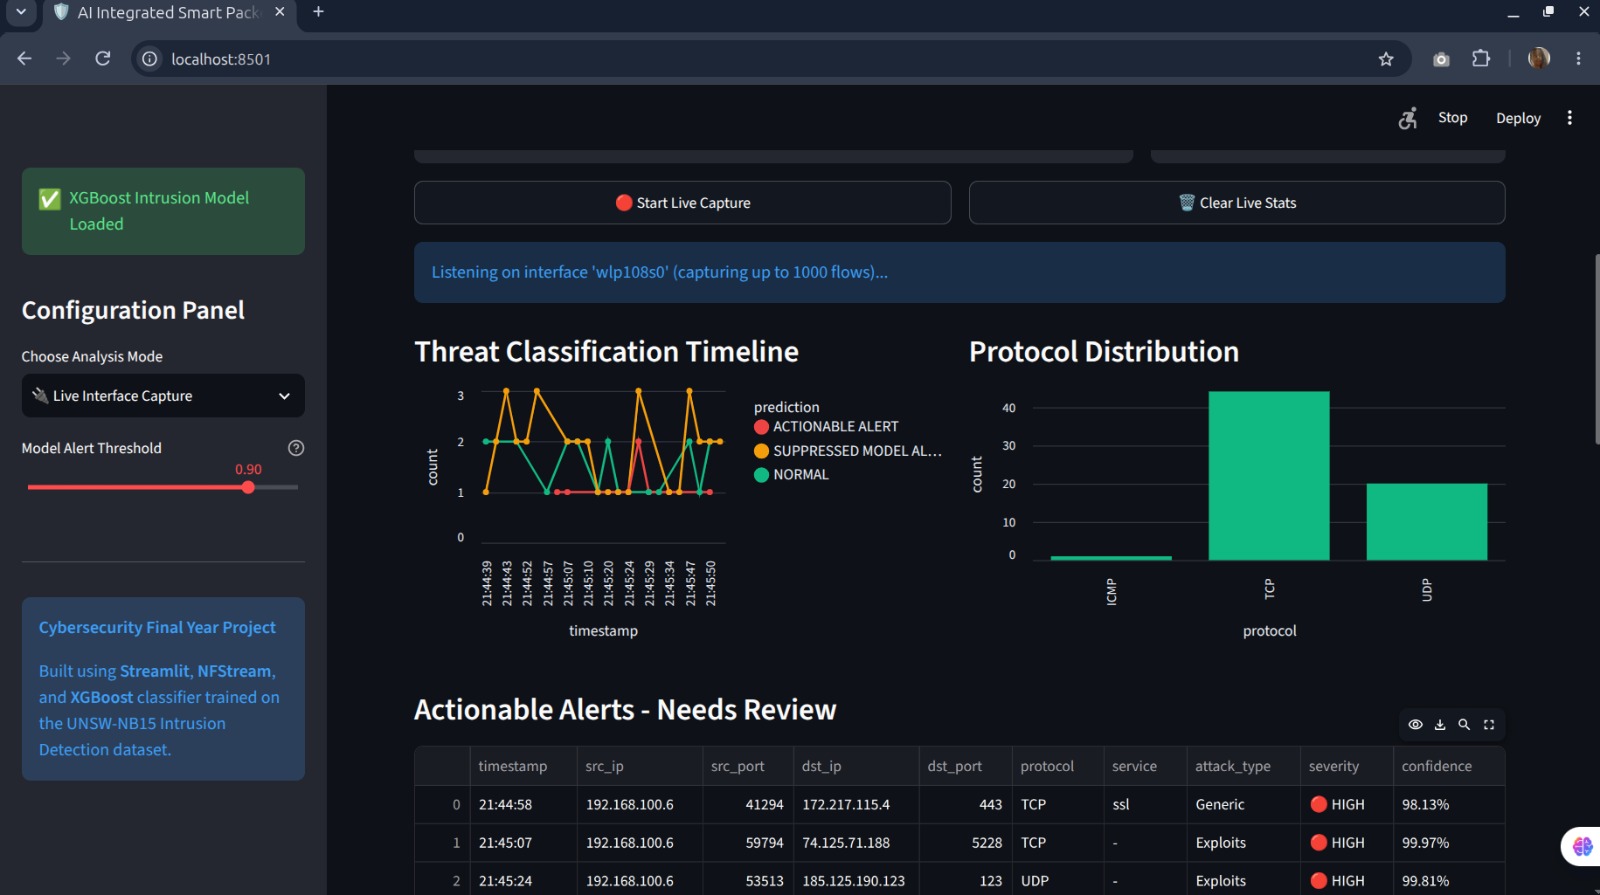
AI Integrated Smart Packet Analyzer

A high-performance Machine Learning Network Intrusion Detection System (NIDS) designed to analyze network flows in real time, distinguish malicious traffic from normal operations, categorize threats, and provide explainable attribution behind every prediction.

  • Evaluated on 82,332 held-out UNSW-NB15 benchmark network flows
  • Binary attack detection and multi-class threat classification with XGBoost
  • Real-time packet inspection via NFStream and Scapy with explainable prediction scoring
  • SOC-style triage dashboard with exportable incident logs and PDF/CSV compliance reports
PythonXGBoostStreamlitNFStreamScapyThreat Intelligence
Read the Full Case Study → View Research & Code on GitHub
Active Client Delivery Commercial Delivery Record

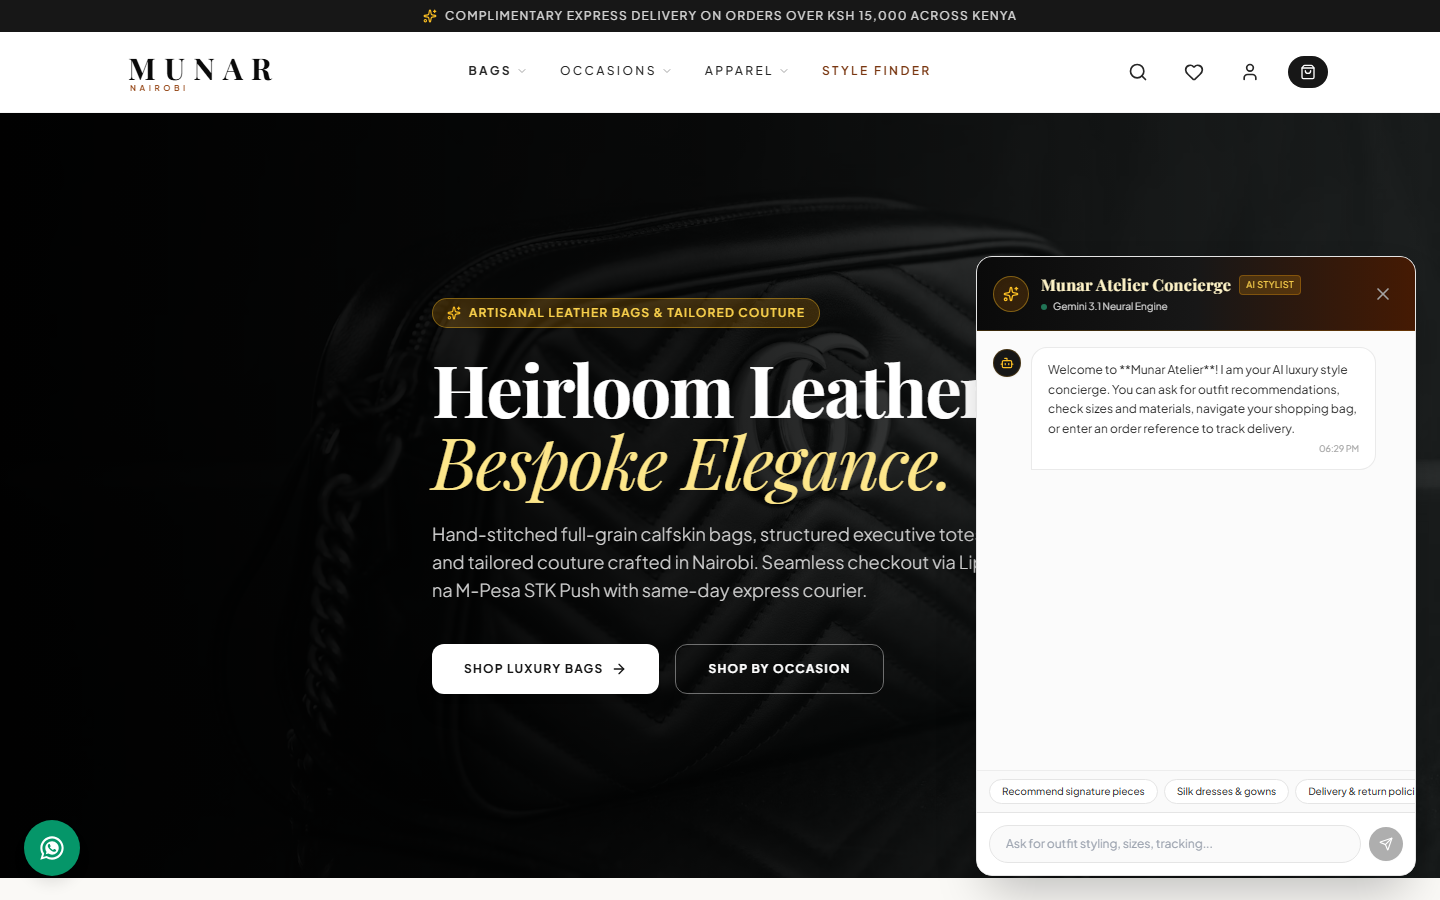
Munar: Website Audit, Optimization & Deployment Handover

Collaborative delivery project with Harrison Ndeke for Munar (munar-ke.vercel.app). Managed the security baseline, content structure, UX clarity, accessibility, technical SEO foundations, and production deployment on Vercel.

  • Established baseline audit across performance, mobile responsiveness, and headers
  • Enforced security boundary: scoped reviews without intrusive unauthorized scanning
  • Implemented structured data, canonical URLs, and clean analytics without tracking leaks
  • Delivered client access, documentation, and maintainable handover record
Client DiscoverySecurity BaselineTechnical SEOUX / Mobile AuditingVercel
Read the Full Case Study → View Munar Deployment
HarLyn Internal Product · Built & Tested Zero-Trust Data Protection Engine

TrustCapsule: Zero-Trust Data Protection & Audit Trails

Internal data escrow product built with Harrison Ndeke under HarLyn Digital Partners. Wraps outbound sensitive files into self-destructing, watermarked, tamper-proof capsules with audit-trail reports generated from real audit-chain data.

  • AES-256-GCM encryption at rest, forced row-level security, zero permissive policies
  • Append-only HMAC-SHA256 audit chain — even the service role cannot rewrite history
  • 256-bit recipient access tokens, never logged, only stored as a hash
  • Audit-trail reports generated from real audit-chain data
Next.js 15Supabase / Postgres RLSAES-256-GCMChrome ExtensionWordPress Integration
Read the Full Case Study →
In Active Development AI-Assisted Security Monitoring Platform

HarLyn Sentinel: AI-Assisted Security Monitoring Platform

Managed threat-detection and SOC platform in active development with Harrison Ndeke, combining Wazuh telemetry with AI-enriched alerting and automated n8n response workflows — designed for businesses without an in-house SOC.

  • Wazuh-powered log analysis, file integrity monitoring, and vulnerability scanning
  • AI Security Analyst converts raw alerts into plain-English risk context and attack-chain mapping
  • Red-team / blue-team simulation lab for validating detection rules before customer rollout
  • Separate SOC console and client executive dashboard with monthly compliance reporting
WazuhNext.js 15n8nMulti-Tenant Architecture
Read the Architecture Record →
View All Technical Proof & Case Studies → See what's in development →

PUBLICATIONS & CASE STUDIES Technical Field Notes & Research

Evidence-led incident walkthroughs, authorized threat triage field notes, and regulatory engineering blueprints for high-growth African enterprises.

View All Field Notes & Research →

PRACTICE Learning & Security Work

Jul 2023 to Sep 2026

Zetech University

B.S. in Computer Science

Rigorous focus on computer systems, algorithm design, software engineering architectures, database security, and networking protocols.

Mar 2023 to Present

GOMYCODE

Diploma in Cybersecurity

Applied laboratory coursework in network defense, authorized penetration testing methodologies, vulnerability assessments, incident triage, and cryptography.

How Security Work Is Done

Authorized, Evidence-Led Assessments

Written scope, OWASP-aligned checks, reproducible findings, and a prioritized fix list.

Founding Cross-Training Rhythm

Nazline Mwita and Harrison Ndeke · Bi-weekly technical exchange
ACTIVE CURRICULUM
Nazline Teaches:
  • Threat modeling & security baselines
  • Web and API vulnerability assessment
  • Authorised testing methodology & scoping
  • Evidence, severity rankings & remediation
  • Data privacy & incident response fundamentals
Harrison Teaches:
  • APIs, webhooks & data-flow architecture
  • n8n workflow design & error handling
  • AI agents, tools & RAG systems
  • AI-powered website systems & AEO
  • Observability & client handovers

Frequently Asked Questions

Who is Nazline Mwita?

Nazline Mwita is a Cybersecurity Assurance Lead and Co-Founder of HarLyn Digital Partners, based in Nairobi, Kenya. She advises African enterprises on data protection site audits, authorized web and API security assessments, and secure AI and automation architecture.

What does a Cybersecurity Assurance Lead do?

A Cybersecurity Assurance Lead verifies that an organisation's systems, data flows, and automated workflows actually behave as claimed. Nazline Mwita's assurance work covers authorized vulnerability assessment against OWASP Top 10 and API Security Top 10, data protection site audits, permission and credential audits for AI agents, and evidence-backed remediation roadmaps.

What is a data protection site audit?

A data protection site audit is a technical check of how a website handles visitor and customer data: forms, cookies and consent banners, encryption, access controls, third-party sharing and breach logs. You receive findings and a fix list. This is not legal advice; legal questions belong to an advocate.

Does Nazline Mwita perform unauthorized security testing?

No. All security assessments are conducted strictly under written rules of engagement with documented scope and client authorization. The practice operates on a permission-before-testing standard and does not conduct intrusive or unauthorized scanning of systems outside an agreed scope.

How do I start an engagement with Nazline Mwita?

Most engagements begin with the Secure Digital Workflow Assessment, a fixed-scope two-to-three-week discovery engagement. It maps one critical workflow, public web surface, or internal API, produces authorized security findings, ranks automation opportunities, and delivers a 30/60/90-day remediation roadmap with no obligation to proceed to follow-on build work.

ENGAGEMENT INTAKE Scoped Consultation & Assessment Intake

Interested in our Secure Digital Workflow Assessment, an authorized web/API review, or secure automation design? Submit your project context below. All inquiries are held in strict confidence.

WhatsApp