
"Governance is not a compliance checkbox bolted on after deployment. It is the decision process that determines whether an AI system should exist in production at all."
Boards and founders adopting AI often skip straight to procurement and deployment — whose vendor, what model, what budget. Governance gets treated as paperwork for later, if at all. This piece is written for the decision-maker approving that adoption, not the engineer building it.
1. Why Governance Is a Board-Level Question
An AI system making decisions about customers, credit, hiring, or sensitive data carries reputational and regulatory exposure the same way a financial control does. Treating it as a purely technical rollout, decided entirely inside engineering, is how organizations end up explaining an incident after the fact instead of preventing it beforehand.
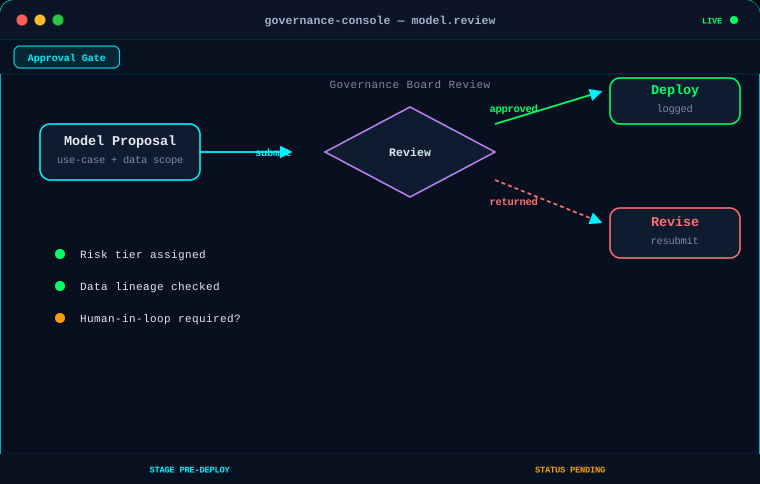
Governance Principle
No AI system reaches production without an explicit, logged approval decision.
2. What an Approval Gate Actually Checks
- Risk tier: what happens if this system is wrong, biased, or manipulated — and who is affected?
- Data lineage: what data trained or feeds this system, and was it lawfully obtained and used?
- Human-in-the-loop requirement: does a consequential decision need a human sign-off before it takes effect?
3. A Practical Board-Level Checklist
| Question | Why it matters |
|---|---|
| Who owns this system's risk? | Without a named owner, incidents get discovered, not managed |
| What is the worst plausible failure? | Sets the review depth the system actually needs |
| Can a decision be appealed or reversed? | Determines whether human oversight is load-bearing or cosmetic |
| Is there a kill switch? | A system without a disable path is a system you can't actually govern |
| Who reviews this again, and when? | Governance is a recurring gate, not a one-time approval |
4. What This Is Not
It is not a vendor's AI ethics statement pasted into a policy PDF. It is not a one-time review at launch with no re-review as the system or its data changes. Governance that doesn't recur isn't governance — it's a launch memo.
Guiding Principle
Start with a named owner and a kill switch. Everything else in a governance program builds on someone being accountable and able to act.
Skills Demonstrated: AI Governance · Risk Oversight · Board Advisory · Approval Process Design
Related service: AI Security · Related: AI Risk Assessment